Cryptographic Architecture & Ciphers
Looking for the encrypted container user guide? See DodaZIP Vault & Secure Containers.
Military-Grade Cryptographic Architecture
DodaZIP replaces aging cryptographic algorithms with modern, high-entropy cipher suites. While legacy utilities continue using vulnerable PBKDF2 key derivation and legacy ZipCrypto, DodaZIP implements XChaCha20-Poly1305 and AES-256-GCM authenticated encryption with Argon2id key derivation.
🔐 Why Legacy Archiver Encryption Fails
Most users assume that password-protecting an archive in traditional software guarantees security. In reality:
| Flaw in Legacy Archivers | Security Vulnerability | The DodaZip Solution |
|---|---|---|
| PBKDF2 Key Derivation | Vulnerable to consumer GPU / ASIC rigs (cracks billions of hashes/sec). | Argon2id KDF requires large physical memory buffers, neutralizing GPU cracking clusters. |
| Unencrypted Metadata | Filenames, file counts, and timestamps remain in plaintext in the header. | Full Metadata Shield: Filenames, directory hierarchies, and sizes are completely encrypted. |
| No Integrity Authentication | An attacker can alter bits in an encrypted archive without detection. | Poly1305 / GCM AEAD: Any tampering or byte alteration triggers an instant authentication failure. |
| Legacy ZipCrypto Mode | Broken in minutes using standard open-source tools (e.g. bkcrack). | No Weak Fallbacks: DodaZIP refuses to create insecure legacy encryption. |
🛡️ Technical Implementation
1. Key Derivation Function (KDF): Argon2id
- Winner of the Password Hashing Competition (PHC).
- Configured with memory-hard cost parameters (
m_cost = 64 MB,t_cost = 3 iterations,p_cost = 4 parallel threads). - Combines data-independent memory access (defending against side-channel cache timing attacks) and data-dependent memory access (defending against GPU cracking rigs).
2. Authenticated Encryption with Associated Data (AEAD)
- Primary Cipher: XChaCha20-Poly1305
- Stream cipher with an extended 192-bit (24-byte) nonce generated directly from the operating system’s Cryptographically Secure Pseudorandom Number Generator (CSPRNG).
- Eliminates the risk of nonce collisions even across millions of encrypted archives.
- Poly1305 generates a 128-bit authentication tag per chunk to guarantee message integrity.
- Alternative Standard: AES-256-GCM
- Full hardware-accelerated AES-NI encryption with Galois Counter Mode verification.
💻 Usage
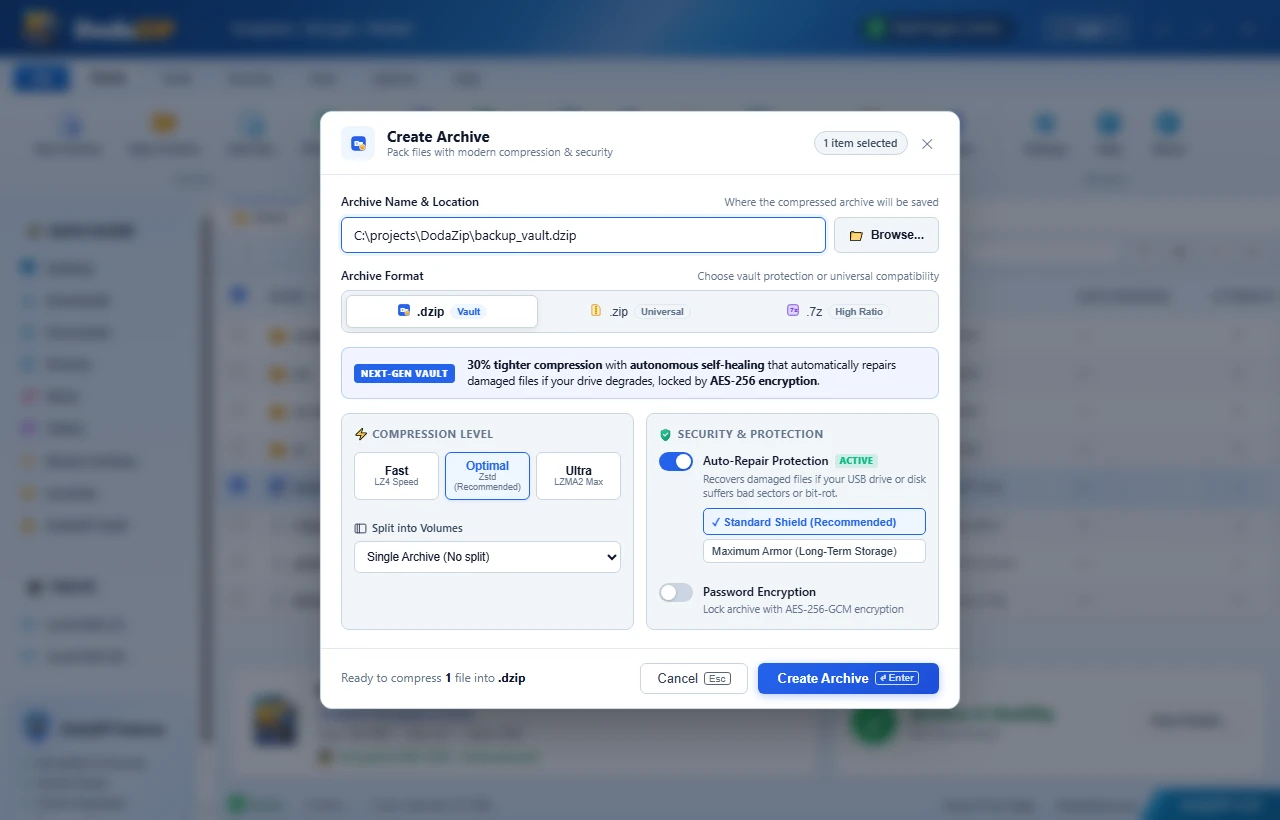
Via Desktop GUI
- In the Create Archive modal, check the Encrypt Archive box.
- Enter your master password.
- Choose your preferred cipher: XChaCha20-Poly1305 (recommended) or AES-256-GCM.
- Both file contents and directory listings will be encrypted.
Via Command-Line Interface (CLI)
# Interactive secure password prompt
dodazip c -i ./confidential-docs -o secure-vault.dzip --password "YourMasterSecret123"

# Specify cipher algorithm explicitly
dodazip c -i ./database-backup -o db.dzip --password "SecretKey" --cipher xchacha20
⚠️ Cryptographic Notice
DodaZIP adheres to zero-knowledge cryptographic standards:
- Passwords and encryption keys are processed in memory and never written to disk or transmitted over networks.
- There is no backdoor or master recovery mechanism. If the password is forgotten or lost, the data is mathematically unrecoverable.